Most engineering and technical firms do not notice their IT setup was built for one office until they open a second.
At 15 or 20 staff under one roof, almost anything works. Files sit on a local server or a shared drive everyone can see. The office network is fast and reliable. If something breaks, someone walks over and looks at it. None of that survives the move to a second site, a remote project office, or a growing field team, and the firms that feel this hardest are the ones whose work depends on real operational complexity: multiple projects, multiple locations, and people who need the same information whether they are at head office or three hours up the highway.
This is a growth story more than an IT one. IT is usually just where it shows up first.
The systems that felt effortless in one office were never actually simple, they just had the benefit of everyone being in the same building. A shared drive works because someone can walk over and ask who has a file open. Support works because a problem can be seen and touched. None of that was ever written down as a plan, so nobody notices it was a plan at all, until a second office removes the thing that was quietly holding it together: proximity.
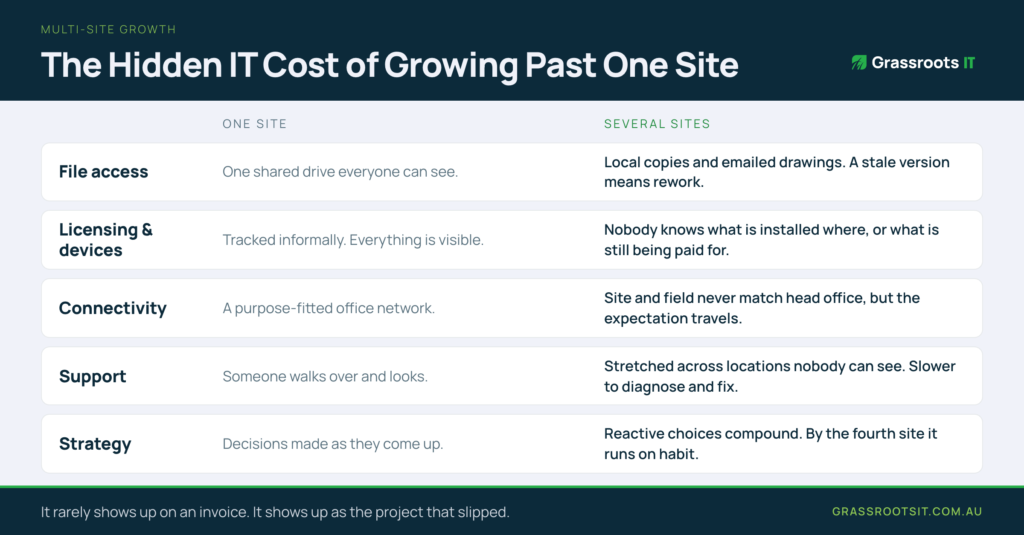
File access and version control.
One site: a shared drive or local server that everyone can see and everyone understands. Several sites: staff end up working from local copies, emailing drawings back and forth, or losing time waiting for a connection back to head office just to open a file. On a technical project, a stale version of a drawing is not a minor inconvenience: it means rework, and sometimes a mistake that reaches a client.
Licensing and device management.
One site: software licences tracked informally, because everyone and everything is visible. Several sites: nobody quite knows what is installed where, what is still being paid for, or what is out of date on a laptop that has not been back to head office in months. The cost is never dramatic on any single machine; it accumulates quietly across dozens of them.
Connectivity.
One site: a purpose-fitted office network that just works. Several sites: site offices and field locations rarely get the same reliability, but the expectation that systems “just work” travels with the team anyway, and every dropped connection becomes a support call.
Support.
One site: an informal arrangement, internal or outsourced, sized for one location and one set of problems. Several sites: the same person or provider is now stretched across locations they cannot see, with issues that take longer to diagnose and longer again to fix, because half the job used to be walking over and looking.
Strategy.
One site: infrastructure decisions made as they come up, because the stakes of getting one thing wrong are low. Several sites: those same reactive, site-by-site decisions compound. Each new site adds a bit more complexity to a setup that was never designed to scale, and by the third or fourth site the whole thing is being held together by habit rather than design.
Hardware is beside the point. What matters is whether your systems were designed to support one site or several. A setup built for growth typically has a few things in common: a centralised, cloud-based environment that any authorised person can reach securely from any location, standardised device management so every laptop and site machine meets the same baseline regardless of where it sits, connectivity planned for field and site conditions rather than assumed to match head office, and an IT partner who is thinking about your next site before you open it, not reacting once it is already causing problems.
The firms that get ahead of this treat IT as part of the growth plan itself, rather than something to patch once the second office is already open and struggling. It is a small mindset shift with an outsized payoff: the same investment made a year earlier costs roughly the same, but made a year later it is competing with lost hours, duplicated work, and frustrated staff who have already worked around the problem in their own, less reliable ways.
A simple test is whether your current setup would survive being copied and dropped into a second location tomorrow. If the honest answer involves a password taped to a monitor, a folder structure only one person really understands, or a support arrangement that quietly assumes someone can walk over and look, that is where the real cost is hiding. It rarely shows up on an invoice. It shows up as the project that slipped, the drawing that was a version behind, or the new hire at the second site who spent their first week unable to access half of what they needed.
If you are looking at a new site, a growing field team, or you have already opened one and are feeling the strain, it is worth having that conversation before the next expansion rather than after. We have spent two decades working with engineering and technical firms across South East Queensland through exactly this kind of growth, and the pattern is consistent: the cost of fixing this properly barely changes with time, but the cost of leaving it keeps climbing the longer it sits.
Grassroots IT is a Brisbane-based managed IT services provider specialising in Microsoft solutions for engineering and technical firms across South East Queensland. Learn more about our Cloud Services or IT Support.
Your security tools might be doing their job. The question is whether you can demonstrate that to anyone who asks.
There’s a version of cybersecurity that feels solid from the inside but falls apart the moment someone asks you to account for it. The tools are there. The IT team or provider is on top of things. Nothing has gone wrong. And yet, if a cyber insurer, an enterprise client, or your own board asked you to demonstrate your security posture tomorrow, you’d struggle to know where to start.
This is more common than most business owners realise, and it’s becoming a genuine liability. Here are five signs you might be in this position.
Cyber insurance is the most immediate place this shift is showing up. Not long ago, insurers would run through a checklist at renewal: multifactor authentication, regular patching, offsite backups. A yes across the board and you’d get your policy.
That process has changed substantially. Australian cyber insurance underwriting tightened significantly through 2024 and 2025. The informal tick-and-flick application form has been replaced by detailed technical questionnaires, and for higher cover, evidence of controls. Businesses that haven’t invested in structured security practices are increasingly finding that cyber insurance is either expensive or simply unavailable.
The market is also about to get more costly. After two years of softening rates, S&P Global forecasts a 15 to 20 per cent premium increase in 2026. Organisations with strong, documented security postures will be better placed to negotiate favourable terms. Those without them won’t.
There’s also a significant coverage gap that most business owners aren’t aware of. Only 10 to 20 per cent of businesses currently carry cyber insurance, compared to 40 to 50 per cent of mid-market firms. That means the majority of small businesses are carrying a risk they’ve largely left unquantified, and uninsured.
The procurement picture is similar. If your business sells to enterprise clients or operates in regulated industries like financial services or healthcare, you may already be fielding questions about your security posture from clients or partners. Insurers are increasingly requesting third-party security attestations, such as framework certifications or maturity assessments, for cover above $1 million. That expectation is spreading beyond the insurance conversation into tenders, contracts, and supplier assessments. It only moves in one direction.
Staff awareness training is one of the most consistently underestimated controls in a small business security program. It’s also one of the first things that gets asked about in an insurance renewal or a client security questionnaire.
A single induction session from two years ago doesn’t count. Neither does a policy document that lives in a shared drive nobody reads. What insurers and certification frameworks are looking for is evidence of regular, completed, documented training: monthly or quarterly cycles, completion tracking, and accountability for non-completion. If you can’t point to records showing your team is actively engaged with security awareness on an ongoing basis, that’s a material gap regardless of how good your technical controls are.
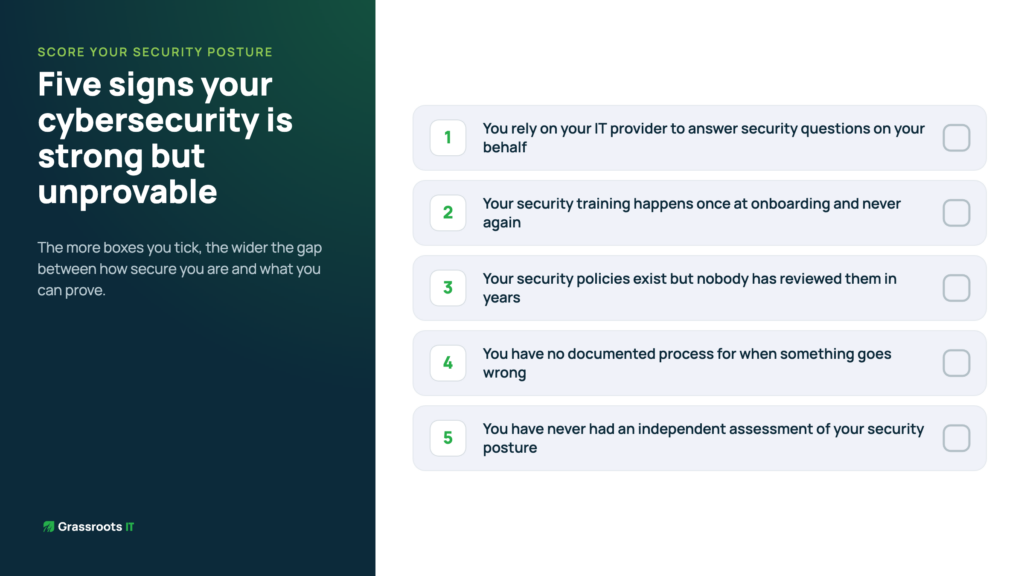
Most businesses at the 30-to-100-staff mark have some version of a password policy, an acceptable use policy, and possibly an incident response plan. What’s less common is any evidence that those documents are current, reviewed regularly, or actually reflect how the business operates.
Outdated policies are a problem for two reasons. First, they may no longer cover the tools, platforms, and working arrangements the business actually uses. A policy written before the shift to hybrid work and cloud storage is almost certainly missing something. Second, they signal to anyone reviewing your security posture that governance is informal, not a managed process. A document dated 2021 that hasn’t been touched since tells its own story.
Most small businesses have a rough idea of what they’d do in the event of a cyber incident: call the IT provider, shut things down, figure it out from there. What most don’t have is a documented, tested incident response plan that assigns roles, defines communication protocols, and sets out a recovery sequence.
This matters more than it might seem. Cyber insurers ask about it directly. More practically, when something goes wrong is the worst possible time to be working out who does what. Businesses that have rehearsed their response, even in a basic tabletop exercise, consistently handle incidents faster and with less collateral damage than those that haven’t. The plan doesn’t need to be long. It needs to exist and be known.
Internal confidence is not the same as verified maturity. Most businesses that haven’t had an external assessment tend to overestimate their position in some areas and have genuine blind spots in others. That’s not a criticism. It’s simply what happens when you’re assessing your own work without a reference standard.
An independent gap assessment against a recognised framework gives you something internal review can’t: a clear, objective picture of where you stand, what’s missing, and how significant the gaps are. For most businesses, the result is more reassuring than expected. The foundations are usually stronger than they think. The gaps tend to be in documentation and formalisation, not in the underlying controls. But until you’ve done the assessment, you’re operating on assumption.
Good cybersecurity and demonstrable cybersecurity are not the same thing. You can have genuinely strong security practices and still be unable to account for them in any meaningful way to an insurer, a client, or a board. That gap is closing as expectations rise, and the businesses that close it proactively are in a significantly better position than those that wait until someone asks.
If any of the five signs above felt familiar, it’s worth understanding where your business actually sits. An independent assessment is a reasonable first step, and for most businesses, the picture is clearer and more manageable than they expect.
Ready to move from research to action? The first step is understanding where you currently stand. A baseline security assessment can break decision paralysis by giving you concrete starting point. Contact us today to discuss your current cybersecurity posture and next best steps forward.
“Pretty secure” isn’t good enough anymore.
That’s the uncomfortable truth we put to our LinkedIn audience recently, and the response told us it landed. Because most businesses answer the cybersecurity question the same way: do we have antivirus, backups, MFA? Yes, yes, yes. So we’re pretty secure, right?
The problem is that “pretty secure” is doing a lot of heavy lifting. Cyber insurers don’t accept pretty secure. Enterprise clients putting you through procurement don’t accept pretty secure. And when something goes wrong, pretty secure won’t hold up in a board conversation either.
The shift happening right now is from cybersecurity as a tool checklist to cybersecurity as something you can actually demonstrate. Not describe. Demonstrate. That’s a different question entirely, and most businesses aren’t ready for it yet.
We spent the last six months getting ready for it ourselves. Here’s what that looked like, and what it means for your business.
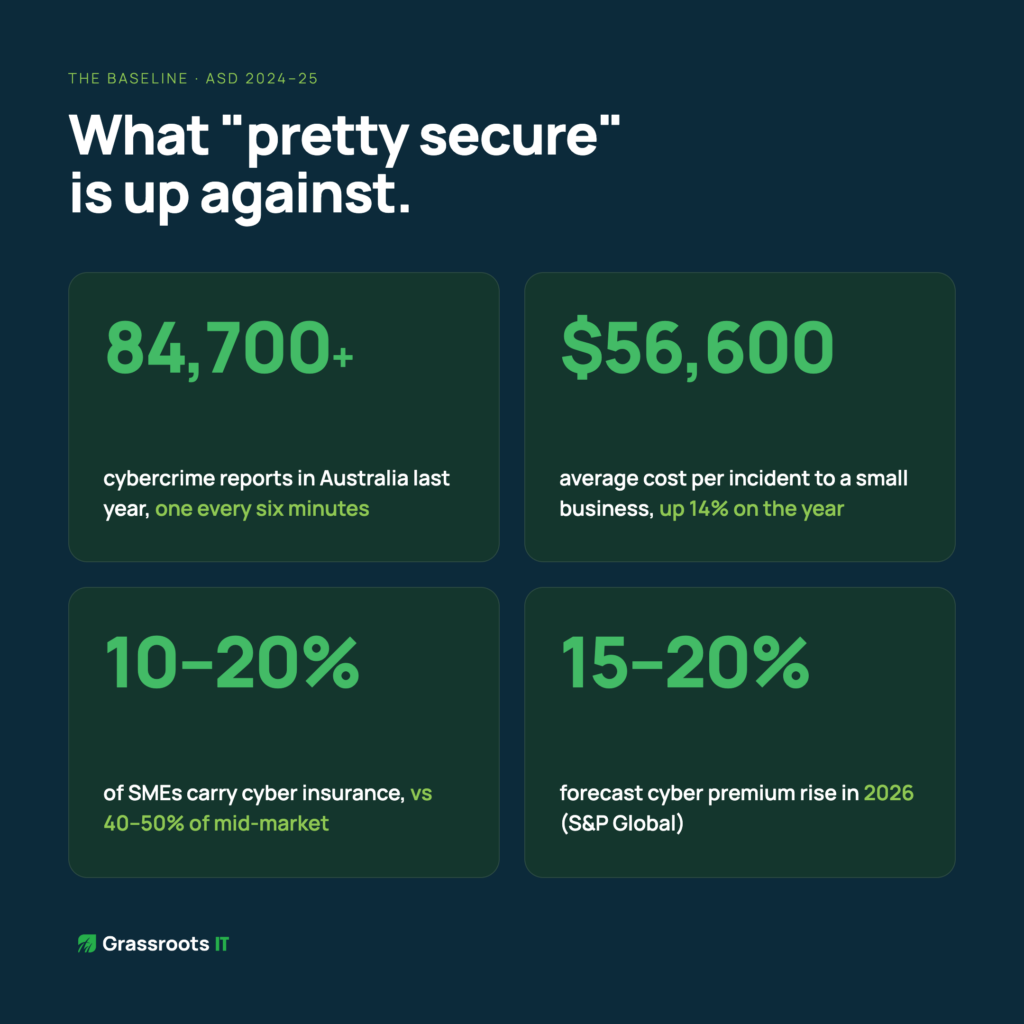
Before we get to the insurance conversation, it helps to understand the baseline. The ASD’s 2024-25 Annual Cyber Threat Report recorded over 84,700 cybercrime reports in Australia last financial year, one every six minutes, with the average cost to small businesses rising 14 per cent to $56,600 per incident. That’s not the cost of a catastrophic breach at a large organisation. That’s the average cost hitting businesses like yours and ours.
What’s notable is how many of those businesses thought they were pretty secure right up until they weren’t.
Cyber insurance is the most immediate place this shift is showing up. Not long ago, insurers would run through a checklist at renewal: multifactor authentication, regular patching, offsite backups. A yes across the board and you’d get your policy.
That process has changed substantially. Australian cyber insurance underwriting tightened significantly through 2024 and 2025. The informal tick-and-flick application form has been replaced by detailed technical questionnaires, and for higher cover, evidence of controls. Businesses that haven’t invested in structured security practices are increasingly finding that cyber insurance is either expensive or simply unavailable.
The market is also about to get more costly. After two years of softening rates, S&P Global forecasts a 15 to 20 per cent premium increase in 2026. Organisations with strong, documented security postures will be better placed to negotiate favourable terms. Those without them won’t.
There’s also a significant coverage gap that most business owners aren’t aware of. Only 10 to 20 per cent of businesses currently carry cyber insurance, compared to 40 to 50 per cent of mid-market firms. That means the majority of small businesses are carrying a risk they’ve largely left unquantified, and uninsured.
The procurement picture is similar. If your business sells to enterprise clients or operates in regulated industries like financial services or healthcare, you may already be fielding questions about your security posture from clients or partners. Insurers are increasingly requesting third-party security attestations, such as framework certifications or maturity assessments, for cover above $1 million. That expectation is spreading beyond the insurance conversation into tenders, contracts, and supplier assessments. It only moves in one direction.
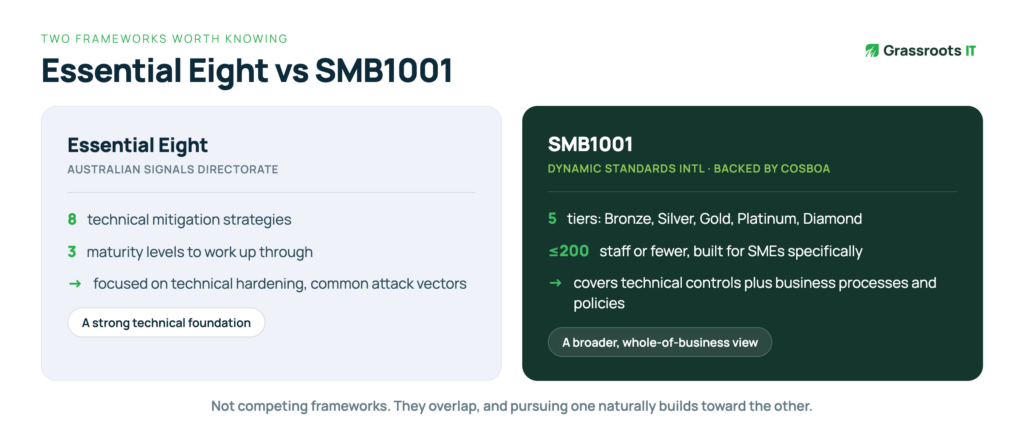
Australia has two well-regarded cybersecurity frameworks that help businesses move from informal security practices to something documented, structured, and verifiable.
The first is the Essential Eight, developed by the Australian Signals Directorate. Most businesses have heard of it. It covers eight technical mitigation strategies across three maturity levels and is designed to reduce the most common attack vectors. It’s a strong technical foundation.
The second is SMB1001, developed by Dynamic Standards International and backed by the Council of Small Business Organisations Australia. It’s less well known, but it was built specifically for businesses of 200 staff or fewer, which makes it more practical for most businesses. SMB1001 runs across five certification tiers, Bronze, Silver, Gold, Platinum, and Diamond, and covers both technical controls and business processes and policies. Where the Essential Eight focuses primarily on technical hardening, SMB1001 takes a broader view of what a mature security posture looks like across an organisation.
They’re not competing frameworks. They overlap significantly, and pursuing one naturally builds toward the other. The right starting point depends on where your business is now and what your most pressing compliance or assurance needs are.
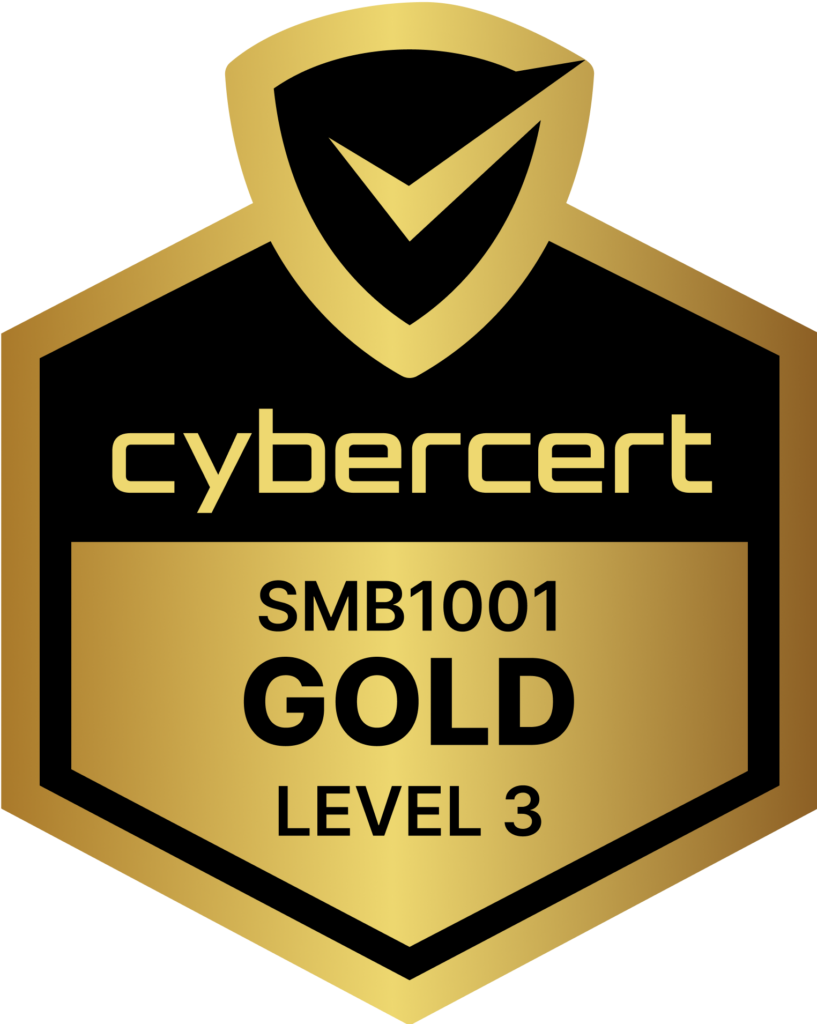
We recently achieved SMB1001 Gold, the third of five tiers. The process took around six months and covered technical uplifts, policy documentation, and third-party vendor accountability.
What it revealed wasn’t a long list of gaps. It was how much good practice we already had in place that simply wasn’t documented. Cyber awareness training that engineers were completing but nobody was formally tracking. Password governance that existed informally but hadn’t been written down. Account management processes that were sound but undocumented. The certification process forced us to formalise what we were already doing, and in doing so, made it auditable, repeatable, and demonstrable to anyone who asked.
That’s a pattern we see consistently across businesses at the 30-to-100-staff mark. The foundations are often stronger than people think. What’s typically missing is the structure and documentation to prove it.
If your cyber insurer, your biggest client, or your board asked you to demonstrate your cybersecurity maturity tomorrow, not describe it, but demonstrate it, what would you be able to show them?
If the honest answer is not much, that’s worth taking seriously. Not because a breach is necessarily imminent, but because the window for getting ahead of this expectation is narrowing. Businesses that can produce evidence of structured, certified security practices are increasingly differentiated in insurance conversations, in procurement processes, and in client confidence.
The good news is that for most businesses, the starting point isn’t as far away as it looks. A gap assessment against either framework will typically show that a significant portion of requirements are already being met. The work is usually in formalisation and documentation, not in building security from scratch.
If you’re not sure where your business sits, a gap assessment is the logical first step. It gives you a clear picture of what you have, what you’re missing, and what a realistic certification pathway looks like, without committing to anything before you understand the scope.
We’re also hosting a webinar shortly that will walk through both frameworks in detail, compare them side by side, and outline what a practical pathway to certification looks like for a Brisbane business. If this is something your business is starting to think about, it’s a worthwhile hour.
Ready to move from research to action? The first step is understanding where you currently stand. A baseline security assessment can break decision paralysis by giving you concrete starting point. Contact us today to discuss your current cybersecurity posture and next best steps forward.
Sources
Australian Signals Directorate, Annual Cyber Threat Report 2024-25, cyber.gov.au
Cliffside, Cyber Insurance Requirements Australia, cliffside.com.au (March 2026)
4iT, Cyber Insurance for Australian businesses in 2026, 4it.com.au (May 2026)