What Is A Cybersecurity Risk Assessment?
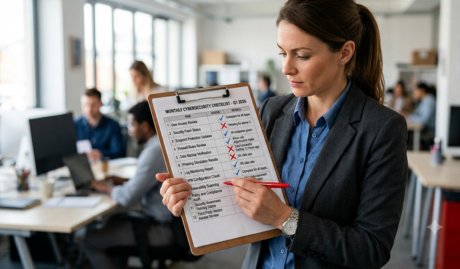
A cybersecurity risk assessment answers two questions in the right order: what could realistically hurt your business, and which of those risks deserve money and attention first. We examine your systems, data, access controls and the habits of the people using them, then weigh each exposure by likelihood and consequence for your operations.
The result is not a scare report. It is a ranked, costed view of your risk, mapped to recognised frameworks like the Essential Eight and SMB1001, so the next security dollar goes where it does the most work.
Why Is A Cybersecurity Risk Assessment So Important?
Because unexamined security is a set of guesses, and the questions are no longer optional. Cyber insurers, major clients and boards now all ask the same thing: show us your risks, and show us what you are doing about them.
A defensible answer for insurers and clients
Insurance questionnaires, tender security sections and board questions all get easier when a current assessment sits behind your answers. We keep findings mapped to the frameworks those audiences recognise: Essential Eight, SMB1001 and ISO 27001.
Priorities instead of anxiety
Every business has more possible security work than budget. An assessment separates the risks that could genuinely interrupt your operations from the ones that merely sound frightening, so decisions rest on evidence rather than the latest headline.
A roadmap you can actually execute
Findings arrive as a prioritised remediation plan with realistic sequencing, not a wall of red. Some items are quick configuration wins; others belong in next year’s budget. We are straightforward about which is which, and we can do the work or hand the plan to your own team.
Why Choose Grassroots IT?
We hold ISO 27001 certification ourselves, so we sit the same exams we set. Our assessments follow the Australian frameworks that actually fit mid-sized businesses, Essential Eight and SMB1001 foremost, rather than enterprise checklists three sizes too big.
And because we implement and operate security controls every day for businesses in Brisbane and beyond, our recommendations arrive priced with real-world effort in mind. If you are after verification of your existing controls rather than a risk-first view, our cybersecurity audit takes that angle.
The Grassroots IT Difference
Dedicated Account Manager
Direct Access To Solution Specialists
Annual Strategy Review & Roadmap
Quarterly Alignment Reviews
Monthly Performance Reporting
Extended Helpdesk Hours
On-Call Emergency Support
Genuine emergencies do not keep office hours. Beyond our extended-hours helpdesk, an on-call arrangement covers urgent after-hours issues, and automated monitoring runs continuously in the background.
Australia-Wide Onsite Support
Dedicated Onboarding Team
Frequently Asked Questions
How often should I undertake a cybersecurity risk assessment?
Annually is the working rhythm, because that is the cycle insurers, auditors and frameworks run on. Bring one forward whenever the ground shifts: a restructure, a new platform, an incident, or a big new contract. An assessment done straight after a change is worth two done on schedule.
Does a cybersecurity risk assessment disrupt business operations?
No. Nearly all of it is reading and reviewing rather than touching: configurations, policies, access lists and logs, mostly through read-only access. Your team’s involvement is a few hours of questions, and nothing changes in your environment during the assessment itself.